
Data protection compliance is now a core part of digital PR, writes Dr. Franklyn Ginger-Eke, who argues that audience trust, not the volume of data a brand holds, will separate the winners.
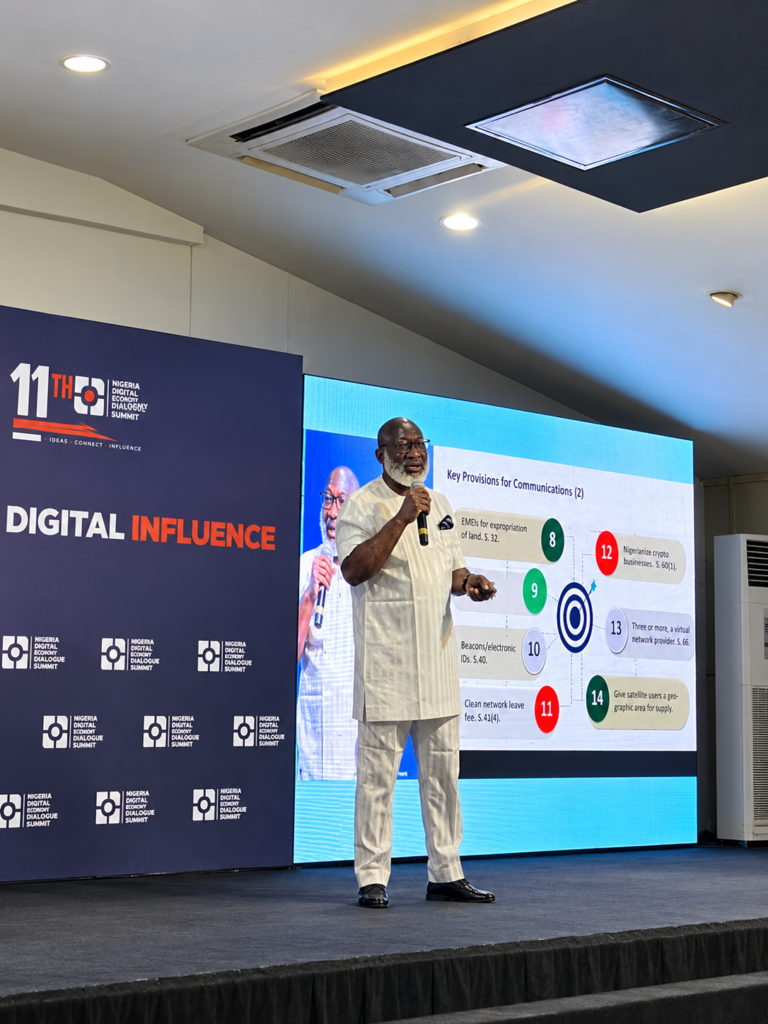
Table of Contents
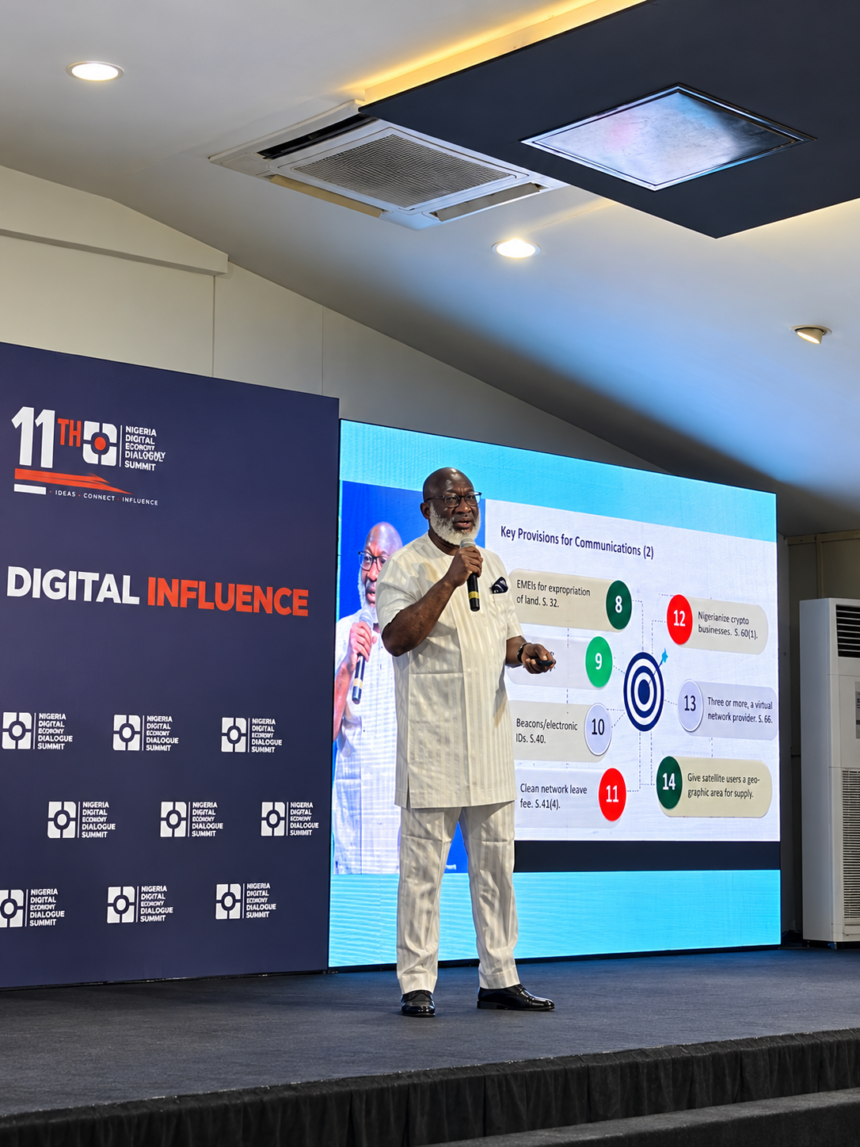
Last Friday in Lagos, at the 11th Nigeria Digital PR Summit, I put a question to a room of communicators, digital influencers, and creators, “What is the most expensive mistake a digital campaign can make today? Not an influencer who ghosts your brand. Not a bad hashtag. Not a trend that fails to catch fire”.
My answer, “It is running an audience-intelligence campaign on borrowed data and unverified consent”.
The regulator has now said as much, in numbers. In September, the National Commissioner of the Nigeria Data Protection Commission (NDPC) told an audience of advertising professionals that only 12.3 per cent of advertising agencies in Nigeria are compliant with the Nigeria Data Protection Act (NDPA) 2023. Simply put, the industry that shapes public narratives has been named a compliance gap.
Every Digital PR Campaign Is a Data Processing Operation
Digital PR now runs on follower data, engagement signals, segmentation, retargeting, social listening and influencer analytics. Every one of these is personal data processing under Nigerian law.
The foundation is Section 37 of the Constitution, which guarantees the privacy of citizens. The NDPA 2023 turns that right into an operating regime. Since 19 September 2025, the NDPC’s General Application and Implementation Directive (GAID) has added the detail, because consent is now required for direct marketing, sensitive data, children’s data, certain cross-border transfers, and automated decisions with compliance and legal effects. Profiling and systematic monitoring call for a data protection impact assessment. That makes every agency, brand and creator a data steward, whether or not they have accepted the role.
What Consent Actually Requires in Digital PR
Consent is not a pop-up. It must be freely given, specific, informed, unambiguous, provable, and as easy to withdraw as to give. Silence, inactivity and pre-ticked boxes do not count, and the burden of proof rests on the organisation, not the audience.
Measured against that standard, familiar digital PR campaign habits look different. “DM to enter” mechanics that harvest contact details with no notice. “Tag a friend” referrals that process the data of people who never dealt with you. Customer lists uploaded to ad platforms for lookalike targeting. Social-listening tools that profile identifiable people with no impact assessment. Youth-facing campaigns with no age gate.
Enforcement is No Longer Theoretical
The NDPC fined MultiChoice Nigeria ₦766 million in July 2025, in part over the processing of data belonging to people who were not even subscribers, and over cross-border transfers, as Reuters reported. It fined Fidelity Bank ₦555.8 million in 2024 after a complaint from a single data subject. Meta has faced a US$263 million penalty order over behavioural advertising and consent, and it has since been settled.
Abroad, the pattern is the same. South Africa’s Information Regulator fined a company for ignoring repeated opt-outs from marketing email. Ireland’s regulator fined Meta €390 million for treating acceptance of its terms as consent to behavioural advertising, as the Data Protection Commission announced. Three lessons are clear, bundled consent fails, consent stretched beyond its purpose fails, and slow-walking the regulator turns a finding into a fine.
There is nuance, too. Consent is not the answer to every question. A South African court recently set aside a fine over published matric results because examination numbers alone did not identify anyone. Asking first whether data identifies a person is good campaign strategy as well as good compliance practice.
A Digital PR Playbook, Not a Panic
None of this argues against audience intelligence in digital PR. It argues for doing it in a way the audience can trust. The playbook I shared has five pillars, namely; consent by design, transparency by default; governance of audience intelligence, accountability for creators and influencers, and trust treated as brand equity, with the discipline to answer the regulator on time.
I advised that Agencies and creators can start complying within thirty days by mapping where audience data enters your business. Replace bundled consent with separate opt-ins. Define your role on each campaign as controller, processor or joint controller, and put data clauses into influencer and vendor contracts. Rehearse a 72-hour breach response, including the holding statement. And appoint an accountable person, but work with a licensed Data Protection Compliance Organisation where registration and audit returns apply.
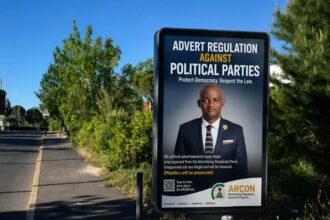
The same compliance questions now touch AI-assisted marketing, as BrandiQ’s report on the FCCPC’s proposed AI marketing rules and NITDA’s warning on AI prompts and corporate data leaks show. Regulators are also watching campaign content itself, as ARCON’s political advertising warning illustrates.
Trust is The Return
What encouraged me most at the Summit was that speakers on very different subjects kept returning to the same two words: reputation and trust. These are the ingredients of influence, and consent by design is how they are earned in a data-driven economy.
The brands that win the next decade will not be those with the most data. They will be the ones their audience trusts enough to keep giving it. Consent is not the cost of digital influence. It is the currency.
Dr. Franklyn Ginger-Eke is the Founder and Chief Strategist of The Rainbow Strategy, a public affairs, strategic communication, and data protection compliance consultant. He is a Fellow of the Nigerian Institute of Public Relations (NIPR) and of the Institute of Information Management.